Services
A complete AI DevSecOps system, not a one-off project
We stand up your AWS infrastructure, your pipelines, and the AI agent layer that operates them — then hand your team the keys. The bootstrap is a day; typical kickoff-to-handoff is 1–2 weeks. It's the same system we run our own production app on.
What we deliver
Every engagement stands up all three layers: infrastructure you own, pipelines that ship it, and governed agents that operate it.
VPC, CloudFront, S3, ECS Fargate, Lambda, Aurora Serverless, Route 53, ACM. All defined in Terraform with Terragrunt orchestration. No ClickOps.
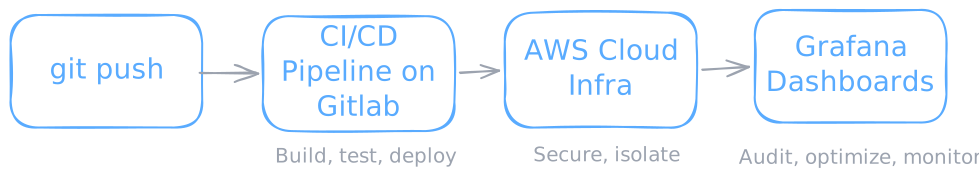
GitLab CI with OIDC federation. Zero static AWS credentials. Multi-arch Docker builds, automatic semantic versioning, and environment-specific deploys.
Claude-powered agents on scheduled sweeps in AWS CodeBuild, on your Claude subscription or through your own Amazon Bedrock. They pick up issues, reproduce bugs, write fixes with tests, and open MRs for human review.
A single-tenant MCP server in your account. Read-only production probes (cost, traffic, alarms, growth) by default; writes gated behind approval tiers mapped to distinct IAM roles.
Grafana dashboards with real-time billing, traffic analytics, geo-visitor maps, and growth metrics — shared by your team and your agents. CloudWatch alarms, CloudTrail audit logs, budget alerts.
A hard spend-breaker that halts runaway agent spend at the platform layer, sleep mode for non-production environments (save up to 60%), budget thresholds with alerts, and free-tier-optimized defaults.
IAM least-privilege roles per tier, OIDC everywhere (no static keys), Terraform deletion guards on production, CloudTrail multi-region logging, and standardized tagging. SOC 2-aligned, and we say exactly what that means.
Dev, staging, and production environments with isolated resources, shared foundations, and an interactive CLI with safety checks and production protection.
Architecture docs, runbooks, and a walkthrough so your team runs it themselves — plus ongoing module, CI template, and dashboard updates delivered to your repos on subscription.
Why Infralista
Proven on a real production app
Chócala — a multi-tenant coaching platform live on TestFlight with real daily users — was built and is operated end-to-end on this exact system: nightly agent sweeps, shared dashboards, tier-gated access, human-gated deploys.
Stood up in a day, not months
Six ordered playbooks take a fresh AWS account to a working agent platform — identity tiers, OIDC, foundations, first environment, agent layer — in a working day. 30+ reusable Terraform modules with feature flags mean you enable only what you need.
You own everything
Infrastructure runs in your AWS account. Code lives in your Git repos. Inference runs on your own meter — Claude subscription or Bedrock. Terraform state is in your S3 bucket. Cancel and it keeps running — no proprietary lock-in, ever.
Not sure what you need?
Book a free call. We'll review your current setup, show you the system running our own app, and map what it looks like in your account. No commitment required.